Publicado el — Deja un comentario

Amazon Connect now supports AWS CloudFormation for message template attachments

Amazon Connect now supports AWS CloudFormation for Outbound Campaign message template attachments, enabling you to create, manage, and deploy these template attachments using AWS CloudFormation. This enhancement allows customers to define and deploy attachments, such as images or documents, as part of the existing MessageTemplate CloudFormation resource.

Message template attachments are used in outbound email campaigns to enrich content and improve engagement. With this launch, customers can now manage attachments programmatically through infrastructure as code, ensuring consistency, repeatability, and automation across staging, test, and production environments.

This feature is available in all AWS Regions where Amazon Connect Outbound Campaigns are supported. For more information, see the AWS Region table. To learn more, see Message templates in the Amazon Connect Administrator Guide or visit the Amazon Connect product page.


​Amazon Connect now supports AWS CloudFormation for Outbound Campaign message template attachments, enabling you to create, manage, and deploy these template attachments using AWS CloudFormation. This enhancement allows customers to define and deploy attachments, such as images or documents, as part of the existing MessageTemplate CloudFormation resource. Message template attachments are used in outbound email campaigns to enrich content and improve engagement. With this launch, customers can now manage attachments programmatically through infrastructure as code, ensuring consistency, repeatability, and automation across staging, test, and production environments. This feature is available in all AWS Regions where Amazon Connect Outbound Campaigns are supported. For more information, see the AWS Region table. To learn more, see Message templates in the Amazon Connect Administrator Guide or visit the Amazon Connect product page.  

Publicado el — Deja un comentario

Desglose de datos de IA: ¿Qué sucede cuando le das Copilot a 20 mil personas?

julio 25, 2025

Desglose de datos de IA: ¿Qué sucede cuando le das Copilot a 20 mil personas?

Lecciones para todos los líderes desde un emblemático experimento del gobierno del Reino Unido.

Gráfico circular compuesto por figuras humanas de colores azul, rojo, verde y amarillo, que representan diferentes categorías o grupos. Algunas figuras están dispersas fuera del círculo principal, indicando posiblemente datos fuera del promedio o categorías adicionales.

Ilustración de Alex Robbins

Esta historia aparece en el boletín de WorkLab. Regístrense aquí.

Todo líder quiere saber: ¿cómo convertir la IA en resultados reales a escala?

En un estudio único en su tipo, el gobierno del Reino Unido entregó Microsoft 365 Copilot a 20 mil empleados durante tres meses. Los hallazgos, basados en los comentarios de los participantes y los datos de uso, ofrecen una visión poco común de cómo funciona la IA a escala en un entorno complejo del sector público. Si bien los resultados reflejan experiencias autoinformadas, sugieren que con el apoyo adecuado, la IA puede ayudar incluso a las organizaciones más grandes a operar más como Empresas Frontera.

Lo que hicieron

La oficina de Servicios Digitales del Gobierno del Reino Unido entregó Copilot a participantes de 12 departamentos, incluidos el Ministerio del Interior, el Ministerio de Justicia y el Departamento de Medio Ambiente, Alimentación y Asuntos Rurales. Los empleados recibieron apoyo de incorporación en forma de preguntas frecuentes, hojas de consejos, videos, sesiones comunitarias y talleres. Para evaluar el impacto, los investigadores del gobierno recopilaron datos de uso y comentarios directos de los empleados.

Los trabajadores del gobierno informan que ahorran tiempo con Copilot

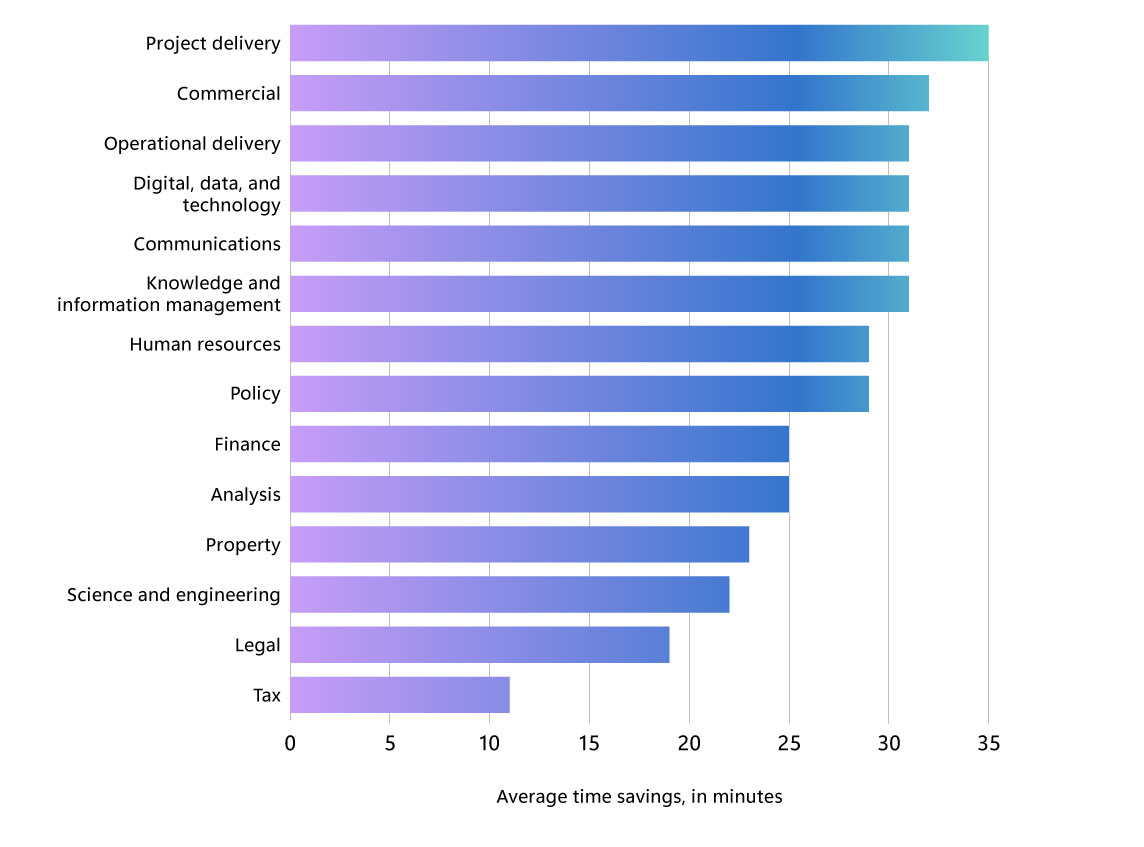
En un estudio de percepción de usuarios del Reino Unido, 20 mil trabajadores gubernamentales que usaron Copilot durante tres meses informaron haber ahorrado tiempo en todos los roles.

Un gráfico de barras que desglosa el ahorro promedio diario de tiempo, por función, para 20,000 trabajadores del gobierno del Reino Unido después de usar Copilot durante tres meses, según una encuesta. El ahorro promedio para todos los trabajadores fue de 25 minutos al día, encabezado por el personal de entrega de proyectos, quienes reportaron ahorrar más de 35 minutos diarios. Las seis funciones principales reportaron ahorros de al menos 30 minutos por día, mientras que los trabajadores del área fiscal reportaron el menor ahorro de tiempo, con 11 minutos diarios.

Lo que encontraron

En promedio, los empleados que participaron en el estudio de percepción del usuario informaron haber ahorrado más de 25 minutos al día con Copilot, casi dos semanas al año. Más del 70% dijo que Copilot les ayudó a dedicar menos tiempo a tareas rutinarias y más tiempo al trabajo estratégico.

Más allá de la productividad, el estudio sacó a la luz un fuerte sentimiento positivo: más del 80% dijo que no querría renunciar a Copilot. Y muchos no tuvieron que hacerlo: nueve de los 12 departamentos optaron por continuar con sus licencias, y desde entonces el gobierno del Reino Unido se ha expandido a 31 mil asientos de Copilot.

Estos resultados se obtuvieron en solo tres meses, de acuerdo con nuestra investigación anterior que muestra que puede llevar hasta 11 semanas comenzar a desarrollar el hábito de la IA. El informe del gobierno del Reino Unido también señala que «hubo fuertes comentarios positivos en torno a los agentes de Microsoft 365 Copilot, con muchos departamentos ansiosos por explorar más la herramienta».

Qué significa

El estudio del gobierno del Reino Unido muestra que la adopción de IA a gran escala no tiene por qué ser lenta. Con una planificación cuidadosa y una orientación reflexiva, las organizaciones pueden desbloquear un impacto significativo en solo unos meses. El ahorro de tiempo reportado equivale a devolver a 1.130 funcionarios públicos un año completo, cada año, para concentrarse en un trabajo de mayor valor.

Para los líderes, el mensaje es claro: la IA puede ofrecer un ROI medible, rápido. Pero el éxito depende de algo más que el acceso: requiere un despliegue intencional y una cultura lista para aceptar el cambio. El enfoque del gobierno del Reino Unido ofrece un modelo de cómo las organizaciones grandes y complejas pueden avanzar para convertirse en empresas de frontera.

The post Desglose de datos de IA: ¿Qué sucede cuando le das Copilot a 20 mil personas? appeared first on Source LATAM.


​The post Desglose de datos de IA: ¿Qué sucede cuando le das Copilot a 20 mil personas? appeared first on Source LATAM.  

Publicado el — Deja un comentario

Announcing readme file support for AWS HealthOmics workflows

Today, AWS HealthOmics introduces enhanced workflow documentation capabilities with the addition of readme file support. This new feature allows bioinformaticians and researchers to attach comprehensive documentation, implementation details, and diagrams directly to their bioinformatics workflows and workflow versions. AWS HealthOmics is a HIPAA-eligible service that helps healthcare and life sciences customers accelerate scientific breakthroughs with fully managed biological data stores and workflows.

The readme file feature improves workflow management by providing a centralized location for critical workflow documentation, enabling more effective knowledge sharing across research teams. Users can now document parameters, input requirements, output formats, and usage instructions within the workflow itself, eliminating the need for separate documentation systems. This capability is particularly valuable for organizations with shared workflows, where multiple scientists need to understand and correctly execute complex bioinformatics pipelines. Readme files can be viewed directly in the AWS Management Console or programmatically accessed via GetWorkflow API calls, and can be updated as workflows evolve.

Readme file support is now available in all regions where AWS HealthOmics is available: US East (N. Virginia), US West (Oregon), Europe (Frankfurt, Ireland, London), Asia Pacific (Singapore), and Israel (Tel Aviv).

To learn more about creating and managing workflow readme files, see the AWS HealthOmics documentation.


​Today, AWS HealthOmics introduces enhanced workflow documentation capabilities with the addition of readme file support. This new feature allows bioinformaticians and researchers to attach comprehensive documentation, implementation details, and diagrams directly to their bioinformatics workflows and workflow versions. AWS HealthOmics is a HIPAA-eligible service that helps healthcare and life sciences customers accelerate scientific breakthroughs with fully managed biological data stores and workflows. The readme file feature improves workflow management by providing a centralized location for critical workflow documentation, enabling more effective knowledge sharing across research teams. Users can now document parameters, input requirements, output formats, and usage instructions within the workflow itself, eliminating the need for separate documentation systems. This capability is particularly valuable for organizations with shared workflows, where multiple scientists need to understand and correctly execute complex bioinformatics pipelines. Readme files can be viewed directly in the AWS Management Console or programmatically accessed via GetWorkflow API calls, and can be updated as workflows evolve. Readme file support is now available in all regions where AWS HealthOmics is available: US East (N. Virginia), US West (Oregon), Europe (Frankfurt, Ireland, London), Asia Pacific (Singapore), and Israel (Tel Aviv). To learn more about creating and managing workflow readme files, see the AWS HealthOmics documentation.  

Publicado el — Deja un comentario

Amazon Connect now supports AWS CloudFormation for quick responses

Amazon Connect now supports AWS CloudFormation for quick responses, enabling customers to deploy and manage quick responses using AWS CloudFormation templates. Quick responses allow contact center agents to access pre-configured messages to respond consistently and efficiently to common customer inquiries. With AWS CloudFormation, administrators can now define and deploy these quick responses across environments in a scalable and repeatable way.

Using AWS CloudFormation, organizations can standardize agent communications and reduce manual configuration between Amazon Connect instances. For example, you can use AWS CloudFormation templates to roll out updated response sets for seasonal campaigns or regulatory compliance across multiple Connect environments. This launch simplifies deployment and integrates seamlessly with continuous delivery pipelines.

This feature is available in all AWS Regions where Amazon Connect is offered. For a full list of supported Regions, see the AWS Region table. To learn more, see Quick responses in the Amazon Connect Administrator Guide or visit the Amazon Connect product page.


​Amazon Connect now supports AWS CloudFormation for quick responses, enabling customers to deploy and manage quick responses using AWS CloudFormation templates. Quick responses allow contact center agents to access pre-configured messages to respond consistently and efficiently to common customer inquiries. With AWS CloudFormation, administrators can now define and deploy these quick responses across environments in a scalable and repeatable way. Using AWS CloudFormation, organizations can standardize agent communications and reduce manual configuration between Amazon Connect instances. For example, you can use AWS CloudFormation templates to roll out updated response sets for seasonal campaigns or regulatory compliance across multiple Connect environments. This launch simplifies deployment and integrates seamlessly with continuous delivery pipelines. This feature is available in all AWS Regions where Amazon Connect is offered. For a full list of supported Regions, see the AWS Region table. To learn more, see Quick responses in the Amazon Connect Administrator Guide or visit the Amazon Connect product page.  

Publicado el — Deja un comentario

Amazon EC2 M8g and R8g instances now available in Asia Pacific (Hong Kong)

Starting today, Amazon Elastic Compute Cloud (Amazon EC2) M8g and R8g instances are available in AWS Asia Pacific (Hong Kong) region. These instances are powered by AWS Graviton4 processors and deliver up to 30% better performance compared to AWS Graviton3-based instances. Amazon EC2 M8g instances are built for general-purpose workloads, such as application servers, microservices, gaming servers, midsize data stores, and caching fleets. Amazon EC2 R8g instances are ideal for memory-intensive workloads such as databases, in-memory caches, and real-time big data analytics. These instances are built on the AWS Nitro System, which offloads CPU virtualization, storage, and networking functions to dedicated hardware and software to enhance the performance and security of your workloads.

AWS Graviton4-based Amazon EC2 instances deliver the best performance and energy efficiency for a broad range of workloads running on Amazon EC2. These instances offer larger instance sizes with up to 3x more vCPUs and memory compared to Graviton3-based instances. AWS Graviton4 processors are up to 40% faster for databases, 30% faster for web applications, and 45% faster for large Java applications than AWS Graviton3 processors.

To learn more, see Amazon EC2 M8g Instances and Amazon EC2 R8g Instances. To explore how to migrate your workloads to Graviton-based instances, see AWS Graviton Fast Start program and Porting Advisor for Graviton. To get started, see the AWS Management Console.


​Starting today, Amazon Elastic Compute Cloud (Amazon EC2) M8g and R8g instances are available in AWS Asia Pacific (Hong Kong) region. These instances are powered by AWS Graviton4 processors and deliver up to 30% better performance compared to AWS Graviton3-based instances. Amazon EC2 M8g instances are built for general-purpose workloads, such as application servers, microservices, gaming servers, midsize data stores, and caching fleets. Amazon EC2 R8g instances are ideal for memory-intensive workloads such as databases, in-memory caches, and real-time big data analytics. These instances are built on the AWS Nitro System, which offloads CPU virtualization, storage, and networking functions to dedicated hardware and software to enhance the performance and security of your workloads. AWS Graviton4-based Amazon EC2 instances deliver the best performance and energy efficiency for a broad range of workloads running on Amazon EC2. These instances offer larger instance sizes with up to 3x more vCPUs and memory compared to Graviton3-based instances. AWS Graviton4 processors are up to 40% faster for databases, 30% faster for web applications, and 45% faster for large Java applications than AWS Graviton3 processors. To learn more, see Amazon EC2 M8g Instances and Amazon EC2 R8g Instances. To explore how to migrate your workloads to Graviton-based instances, see AWS Graviton Fast Start program and Porting Advisor for Graviton. To get started, see the AWS Management Console.  

Publicado el — Deja un comentario

AWS Glue now supports Microsoft Dynamics 365 as a data source

AWS Glue now offers a new native connector for Microsoft Dynamics 365, enabling data engineers to easily integrate data from this enterprise resource planning (ERP) and customer relationship management (CRM) platform. This connector allows AWS Glue users to build efficient extract, transform, and load (ETL) jobs that seamlessly connect to Microsoft Dynamics 365 as a data source.

With this new connector, users can streamline their data integration processes, reducing the complexity and time required to incorporate Microsoft Dynamics 365 data into their AWS-based analytics and business intelligence workflows. Organizations can now leverage the power of AWS Glue’s fully-managed ETL service in conjunction with their Microsoft Dynamics 365 data, enabling more comprehensive insights and data-driven decision-making.

The AWS Glue connector for Microsoft Dynamics 365 is available in all regions where AWS Glue is supported.

To learn more about this new connector and how to get started, visit the AWS Glue documentation.


​AWS Glue now offers a new native connector for Microsoft Dynamics 365, enabling data engineers to easily integrate data from this enterprise resource planning (ERP) and customer relationship management (CRM) platform. This connector allows AWS Glue users to build efficient extract, transform, and load (ETL) jobs that seamlessly connect to Microsoft Dynamics 365 as a data source. With this new connector, users can streamline their data integration processes, reducing the complexity and time required to incorporate Microsoft Dynamics 365 data into their AWS-based analytics and business intelligence workflows. Organizations can now leverage the power of AWS Glue’s fully-managed ETL service in conjunction with their Microsoft Dynamics 365 data, enabling more comprehensive insights and data-driven decision-making. The AWS Glue connector for Microsoft Dynamics 365 is available in all regions where AWS Glue is supported. To learn more about this new connector and how to get started, visit the AWS Glue documentation.  

Publicado el — Deja un comentario

AWS Service Reference Information now supports actions for last accessed services

AWS is expanding service reference information to include information about which service actions are supported by the IAM Last Accessed and IAM Access Analyzer Policy Generation features. IAM Last Accessed and Policy Generator features help you journey towards least privilege permissions, and now you can easily reference which service actions are supported by these features in machine-readable files.

You can automate the retrieval of service reference information, eliminating manual effort and ensuring your policies align with the latest service updates. You can also incorporate this service reference directly into your policy management tools and processes for a seamless integration. This feature is offered at no additional cost. To get started, refer to the documentation on programmatic service reference information.


​AWS is expanding service reference information to include information about which service actions are supported by the IAM Last Accessed and IAM Access Analyzer Policy Generation features. IAM Last Accessed and Policy Generator features help you journey towards least privilege permissions, and now you can easily reference which service actions are supported by these features in machine-readable files. You can automate the retrieval of service reference information, eliminating manual effort and ensuring your policies align with the latest service updates. You can also incorporate this service reference directly into your policy management tools and processes for a seamless integration. This feature is offered at no additional cost. To get started, refer to the documentation on programmatic service reference information.  

Publicado el — Deja un comentario

Announcing Bloom filter support in Amazon ElastiCache

Amazon ElastiCache now supports Bloom filters as a new data type in ElastiCache version 8.1 for Valkey and above. Bloom filters are a space efficient probabilistic data structure that lets you quickly check whether an item is possibly in a set. This new feature is fully compatible with the valkey-bloom module and API compatible with the Bloom filter command syntax of the Valkey client libraries, such as valkey-py, valkey-java, and valkey-go. Previously, to find whether elements were added to your cache, you used the Set data type to write items to a set and then check if that item already existed. Bloom filters achieve the same outcome using a probabilistic approach and are over 98% more memory efficient than using sets without compromising performance.

Bloom filters are available today in Amazon ElastiCache version 8.1 for Valkey in all AWS Regions and for serverless and node-based offerings at no additional cost. To learn more about Bloom filters on ElastiCache for Valkey, check out the ElastiCache documentation. For the full documentation and list of supported commands, see the Bloom filter documentation. 


​Amazon ElastiCache now supports Bloom filters as a new data type in ElastiCache version 8.1 for Valkey and above. Bloom filters are a space efficient probabilistic data structure that lets you quickly check whether an item is possibly in a set. This new feature is fully compatible with the valkey-bloom module and API compatible with the Bloom filter command syntax of the Valkey client libraries, such as valkey-py, valkey-java, and valkey-go. Previously, to find whether elements were added to your cache, you used the Set data type to write items to a set and then check if that item already existed. Bloom filters achieve the same outcome using a probabilistic approach and are over 98% more memory efficient than using sets without compromising performance. Bloom filters are available today in Amazon ElastiCache version 8.1 for Valkey in all AWS Regions and for serverless and node-based offerings at no additional cost. To learn more about Bloom filters on ElastiCache for Valkey, check out the ElastiCache documentation. For the full documentation and list of supported commands, see the Bloom filter documentation.   

Publicado el — Deja un comentario

Amazon Aurora PostgreSQL Limitless Database is now available in 22 additional Regions

Amazon Aurora PostgreSQL Limitless Database is now available in the US West (N. California), Africa (Cape Town), Asia Pacific (Hyderabad, Jakarta, Malaysia, Melbourne, Mumbai, Osaka, Seoul, Thailand), Canada (Central), Canada West (Calgary), Europe (London, Milan, Paris, Spain, Zurich), Israel (Tel Aviv), Mexico (Central), Middle East (Bahrain, UAE), and South America (Sao Paulo) Regions.

Aurora PostgreSQL Limitless Database makes it easy for you to scale your relational database workloads by providing a serverless endpoint that automatically distributes data and queries across multiple Amazon Aurora Serverless instances while maintaining the transactional consistency of a single database. Aurora PostgreSQL Limitless Database offers capabilities such as distributed query planning and transaction management, removing the need for you to create custom solutions or manage multiple databases to scale. As your workloads increase, Aurora PostgreSQL Limitless Database adds additional compute resources while staying within your specified budget, so there is no need to provision for peak, and compute automatically scales down when demand is low.

Aurora PostgreSQL Limitless Database is available with PostgreSQL 16.6 and 16.8 compatibility in these regions.

For pricing details and Region availability, visit Amazon Aurora pricing. To learn more, read the Aurora PostgreSQL Limitless Database documentation and get started by creating an Aurora PostgreSQL Limitless Database in only a few steps in the Amazon RDS console.


​Amazon Aurora PostgreSQL Limitless Database is now available in the US West (N. California), Africa (Cape Town), Asia Pacific (Hyderabad, Jakarta, Malaysia, Melbourne, Mumbai, Osaka, Seoul, Thailand), Canada (Central), Canada West (Calgary), Europe (London, Milan, Paris, Spain, Zurich), Israel (Tel Aviv), Mexico (Central), Middle East (Bahrain, UAE), and South America (Sao Paulo) Regions.
Aurora PostgreSQL Limitless Database makes it easy for you to scale your relational database workloads by providing a serverless endpoint that automatically distributes data and queries across multiple Amazon Aurora Serverless instances while maintaining the transactional consistency of a single database. Aurora PostgreSQL Limitless Database offers capabilities such as distributed query planning and transaction management, removing the need for you to create custom solutions or manage multiple databases to scale. As your workloads increase, Aurora PostgreSQL Limitless Database adds additional compute resources while staying within your specified budget, so there is no need to provision for peak, and compute automatically scales down when demand is low.
Aurora PostgreSQL Limitless Database is available with PostgreSQL 16.6 and 16.8 compatibility in these regions.
For pricing details and Region availability, visit Amazon Aurora pricing. To learn more, read the Aurora PostgreSQL Limitless Database documentation and get started by creating an Aurora PostgreSQL Limitless Database in only a few steps in the Amazon RDS console.  

Publicado el — Deja un comentario

Estrella en ascenso: Conozcan a Dylan, el investigador de seguridad más joven de MSRC

julio 24, 2025

Estrella en ascenso: Conozcan a Dylan, el investigador de seguridad más joven de MSRC

Una persona con traje interactúa con una pantalla transparente flotante

Por: MSRC.

Con solo 13 años, Dylan se convirtió en el investigador de seguridad más joven en colaborar con el Centro de respuesta de seguridad de Microsoft (MSRC, por sus siglas en inglés). Su recorrido hacia la ciberseguridad es inspirador, arraigado en la curiosidad, la resiliencia y un profundo deseo de marcar una diferencia.

Inicios: De cero a la seguridad

La fascinación de Dylan por la tecnología comenzó temprano. Como muchos niños, comenzó con Scratch, un lenguaje de programación visual para hacer juegos y animaciones simples. Pero para Dylan, Scratch era más que un juguete; fue el comienzo de un camino mucho más grande. Muy rápido pasó a HTML y otros lenguajes, y en 5º grado, ya analizaba el código fuente detrás de las plataformas educativas. Un experimento, desbloquear juegos antes de completar las lecciones, lo metió en problemas, pero también despertó un creciente interés en cómo funcionan los sistemas.

Esa curiosidad solo se profundizó durante la pandemia de COVID-19. Cuando su escuela deshabilitó el acceso de los estudiantes para crear reuniones de Teams, Dylan encontró una solución alternativa con Outlook. No se trataba de eludir las reglas, se trataba de ayudar a los compañeros de clase a mantenerse conectados en un momento de aislamiento. Era un vistazo inicial al solucionador de problemas en el que comenzaba a convertirse.

La primera vulnerabilidad de Dylan

Cuando su escuela deshabilitó más tarde los chats de Teams creados por los estudiantes, Dylan no se rindió, se volvió creativo. Lo que comenzó como una búsqueda para restaurar las opciones de comunicación se convirtió en su introducción a la investigación de seguridad. Después de 9 meses de autoaprendizaje, exploración y prueba y error, descubrió una vulnerabilidad que le permitió hacerse cargo de cualquier grupo de Teams. Ese avance marcó su entrada en el mundo de la divulgación responsable e inició su relación con MSRC.

Poco después, Dylan presentó su primer informe oficial de vulnerabilidad a Microsoft. En respuesta, el equipo de Bug Bounty actualizó los términos de su programa para permitir la participación de investigadores de hasta 13 años. Desde entonces, Dylan ha trabajado en estrecha colaboración con MSRC, para demostrar conocimientos técnicos y profesionalismo mucho más allá de su edad.

Colaborar con MSRC

Las habilidades de comunicación de Dylan son tan impresionantes como las técnicas. Es conocido por rechazar de manera respetuosa cuando no está de acuerdo con las evaluaciones iniciales de MSRC, siempre con el objetivo de comprender su perspectiva y articular la suya con claridad. Este enfoque reflexivo le ha ganado respeto y le ha ayudado a obtener resultados significativos.

Un ejemplo notable: Dylan envió una vulnerabilidad en el servicio Authenticator Broker que en un inicio se consideró fuera del alcance. A través de un diálogo claro y constructivo, ayudó a MSRC a comprender sus implicaciones más amplias. ¿El resultado? No solo se reconoció el problema, sino que el programa de recompensas también amplió su alcance para incluirlo en futuras presentaciones, un testimonio del impacto de Dylan.

Desafíos y triunfos

A pesar de sus logros, el camino de Dylan no ha sido fácil. Se ha enfrentado a informes incomprendidos y contratiempos, pero le da crédito a su familia, en especial a su madre, padre, padrastros y abuelos, por ayudarlo a mantenerse con los pies en la tierra, paciente y profesional.

Su recorrido no solo ha sido técnico. Durante la pandemia, Dylan también perdió la voz debido a un problema de salud y se sometió a dos cirugías para recuperarla. La experiencia solo fortaleció su determinación y resistencia.

¿Qué sigue para Dylan?

Ahora en el tercer año de la escuela secundaria, Dylan equilibra el trabajo escolar con actividades extracurriculares como la Olimpiada de Ciencias, las competencias de matemáticas, la natación, el ciclismo y el violonchelo. Presentó 20 informes de vulnerabilidad tan solo el verano pasado, frente a solo seis en total antes.

Ha sido incluido en la lista de investigadores más valiosos de MSRC tanto para 2022 como para 2024. En abril de 2025, Dylan compitió en el Zero Day Quest de Microsoft, un evento de piratería in situ de primer nivel en Redmond, Washington, y se llevó a casa el 3er lugar, un logro increíble que lo colocó entre los mejores investigadores a nivel mundial.

A pesar de una apretada agenda académica, Dylan aun ve la investigación de seguridad como un pasatiempo gratificante. Le apasiona aprender, explorar nuevas vulnerabilidades y retribuir a la comunidad. A largo plazo, está abierto a una variedad de posibilidades, incluido el trabajo continuo en ciberseguridad, ciencia o educación cívica.

Dylan también sueña con asistir a conferencias de seguridad tan pronto como tenga la edad suficiente, ansioso por conocer a otros investigadores y aprender de los mejores. Para otros jóvenes investigadores, su historia es una prueba de que la edad no es una barrera: lo que más importa es la creatividad, la persistencia y la voluntad de aprender.

The post Estrella en ascenso: Conozcan a Dylan, el investigador de seguridad más joven de MSRC appeared first on Source LATAM.


​The post Estrella en ascenso: Conozcan a Dylan, el investigador de seguridad más joven de MSRC appeared first on Source LATAM.